Integrated Healthcare Management System
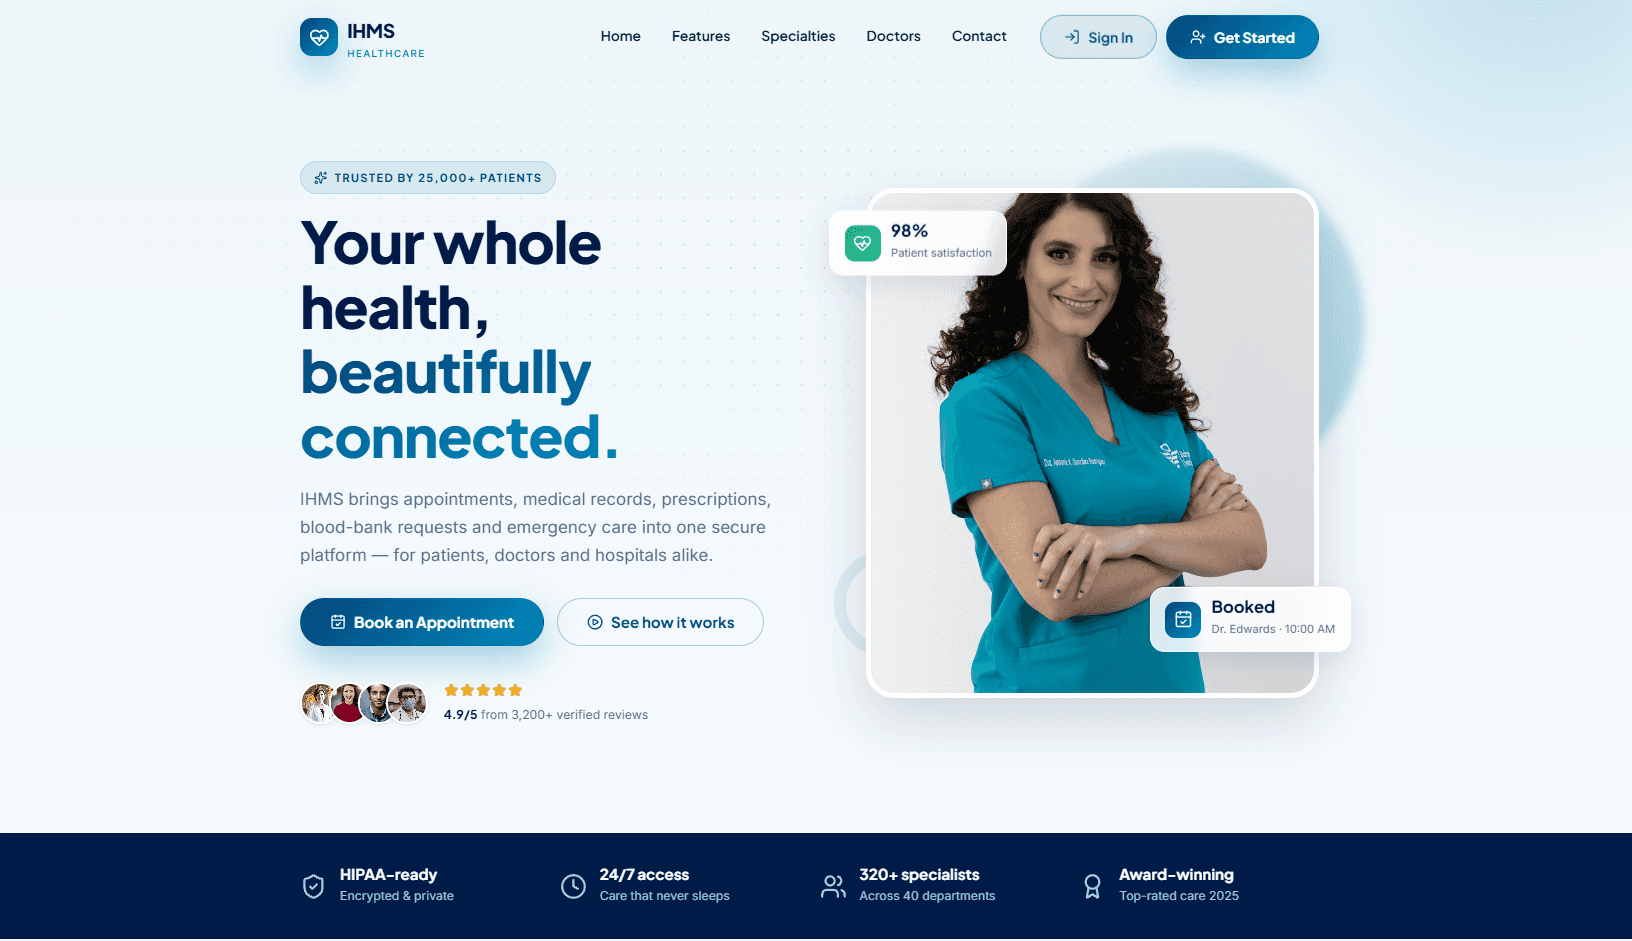
Built on plain PHP and MySQL with no framework, which made every piece of plumbing — routing, sessions, access control, escaping — an explicit decision rather than something inherited. It covers the workflows a small hospital actually runs on, including the ones usually left out of student projects: ambulance booking and a blood bank.
The Problem
Small clinics run on paper and phone calls. Appointments, prescriptions, ambulance requests, and blood-donor contacts each live in a different notebook, so nobody can answer a simple question like which donors match a patient's blood group right now.
The Solution
One database behind role-separated interfaces. Patients book appointments and ambulances and read their own records; doctors manage schedules, prescriptions, and medical history; admins oversee doctors, ambulances, and reports. The blood bank is a self-contained module with its own donor registry, stock view, and request queue.
System Architecture
Every page includes a session guard before it emits any output, so authorisation is decided before a query runs rather than after. A shared Security class centralises the primitives — password_hash at cost 12, random_bytes tokens, htmlspecialchars with ENT_QUOTES for output, filter_var for email — so no page invents its own escaping.
Key Features
Innovative solutions developed to solve complex technical challenges.
Three role-separated dashboards
Patient, doctor, and admin each get their own directory of pages and their own permitted actions, checked per request.
Blood bank module
Donor registry with add, edit, and delete, searchable by blood group, plus a stock view and a request queue for matching donors to needs.
Ambulance dispatch
Patients submit booking requests and track their own; admins manage the fleet and assign vehicles.
Clinical records
Appointments, prescriptions, medical history, health logs, and downloadable reports, each scoped to the patient they belong to.
Reproducible schema
db_migrate.php and db_seed_demo.php rebuild the database and populate demo data, so a fresh checkout reaches a working state without manual SQL.
Challenges & Breakthroughs
Challenge: Without a framework, an unguarded page is a complete authorisation bypass — the URL is the only thing standing between a patient and another patient's records.
Growth: Made the session guard the first include on every page, before any output. Doing the check after rendering has begun is too late to redirect, and that ordering constraint is exactly what a framework's middleware normally enforces for you.
Challenge: Escaping applied ad hoc at each output site gets missed somewhere, and one miss is an XSS hole.
Growth: Centralised it in a Security class with htmlspecialchars(ENT_QUOTES, UTF-8) and recursive array handling, so nested form input is covered by the same call. Consistency matters more than cleverness here — the risk is the site you forget, not the one you write carefully.
Challenge: Six modules touching one schema drift apart quickly when the database is set up by hand.
Growth: Added migration and seed scripts so the schema has a single source of truth in the repository. Being able to reset to a known state turns schema bugs into reproducible ones.
Results & Impact
Next Project
RadFlow